One governance layer. Every obligation, proven.
Find and fix data risk across cloud, on-prem, endpoints, vendors and AI.



integrations
faster vendor assessments
accuracy on automated privacy impact assessments
successful implementations
Six teams. One set of obligations. No shared view.
Every team works from its own spreadsheet about the same personal data.
One platform. Four ways in.
Four products that share one record of your personal data.
Enterprise Governance
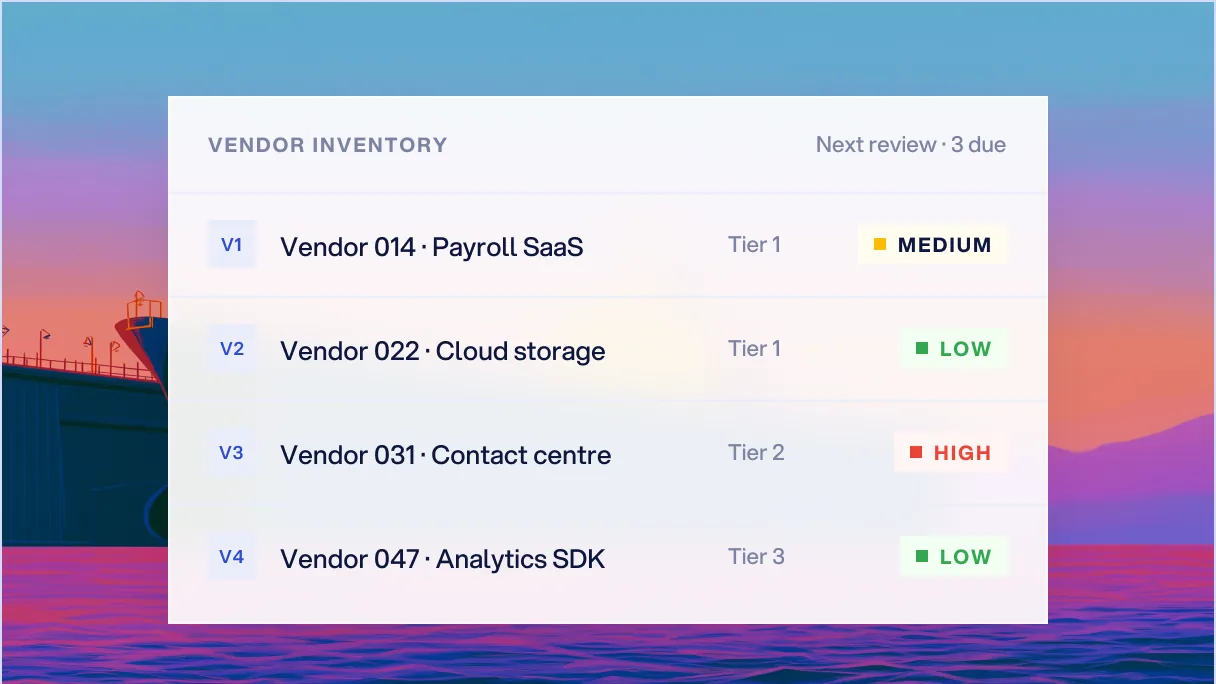
Enterprise risk, assessed with the context you already hold. Answer inbound security questions once instead of every time.
One operating model, from first scan to sealed evidence.
Every step writes to the same connected record.
Discover
Find personal data, classify it, map it, know who owns it.
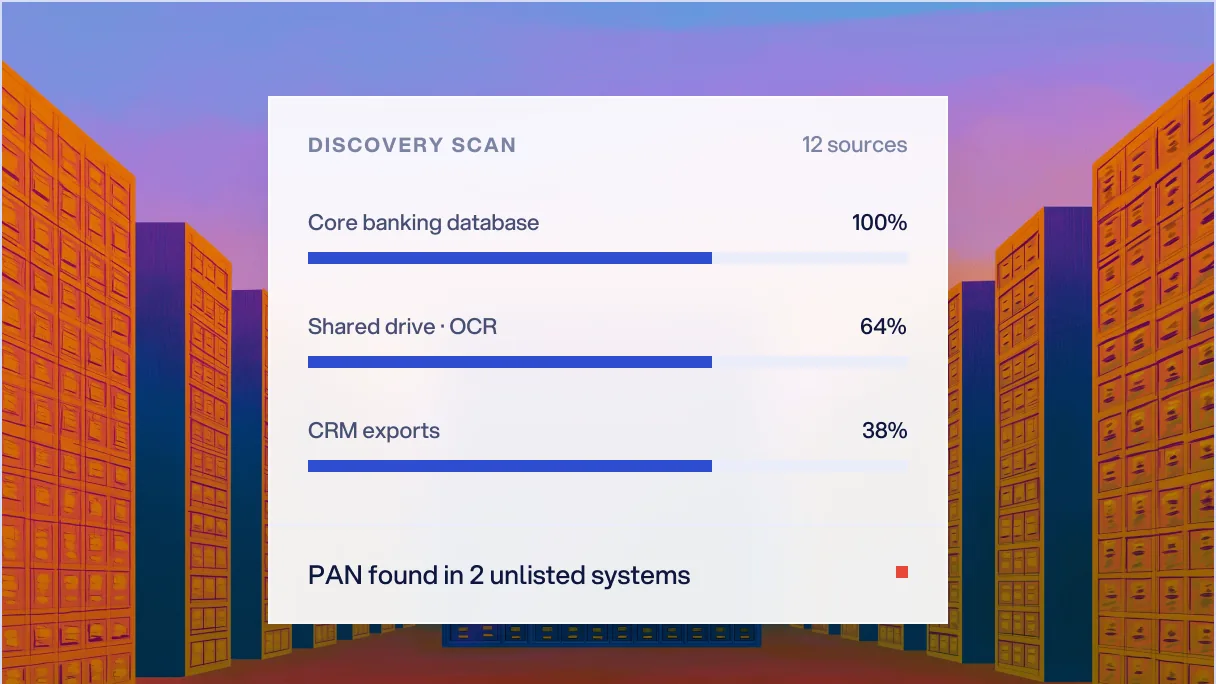
The scan works through each connected source in turn and tags every field it finds.
Govern
Turn findings into living records of purpose, basis, retention, transfers.
Each processing activity gets its own record, updated automatically as sources and vendors change.
Assess
Run DPIAs, transfer assessments and vendor reviews against real context.
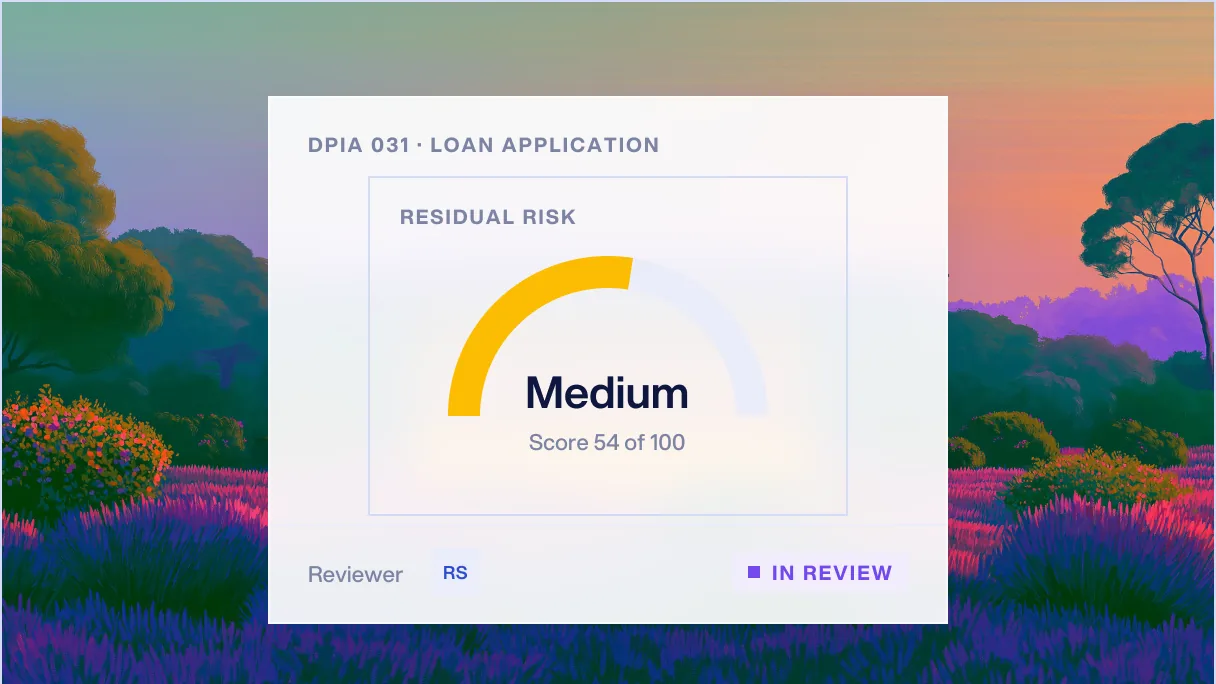
The assessment pulls answers from the connected record instead of asking your team again.
Act
Fulfil rights requests, enforce consent downstream, close incidents.
A rights request opens already knowing where the data lives, and closes when it is done.
Prove
Hold the evidence for every decision, approval and notice version.
Every decision is stored with its source, approver and timestamp, ready the moment it is asked for.
Find one risk.
Everything downstream knows.
Passport numbers turn up on an open shared drive, and every record that depends on it updates.
What Redacto actually does
Redacto does the groundwork. Your team makes the calls.
Scans and classifies personal and sensitive data, including through OCR.
Pulls structured facts out of contracts, policies and vendor documents.
Drafts security questionnaire responses from evidence you already hold.
Scores assessment responses and flags what a person should look at.
Suggests controls, mitigations and risk ratings with the reasoning attached.
Pushes rights requests, deletions and consent withdrawals downstream
Anything that carries risk stops here until a named reviewer signs off.
Decision, source and approver stored together.
Connected to where the business already runs
Plugs into your identity, ERP, procurement, data stores and SaaS
Deployed the way your security team needs it
Hosted and managed by Redacto, live in days, always current.
Redacto runs inside your own cloud account, data never leaves it.
Deployed inside your own data centre, fully under your control.
The controls a security review asks about first.
What protects the record, whichever product writes to it.
SOC 2, ISO 27001, ISO 27701, ISO 42001
Independently audited; SOC 2 report available under NDA.
IAB Europe TCF Registered CMP
Approved status under IAB Europe's Transparency and Consent Framework.
SSO and role based access
People see and change only what their role allows.
Encryption in transit and at rest
Data is encrypted as it moves and where it is stored.
Audit logging
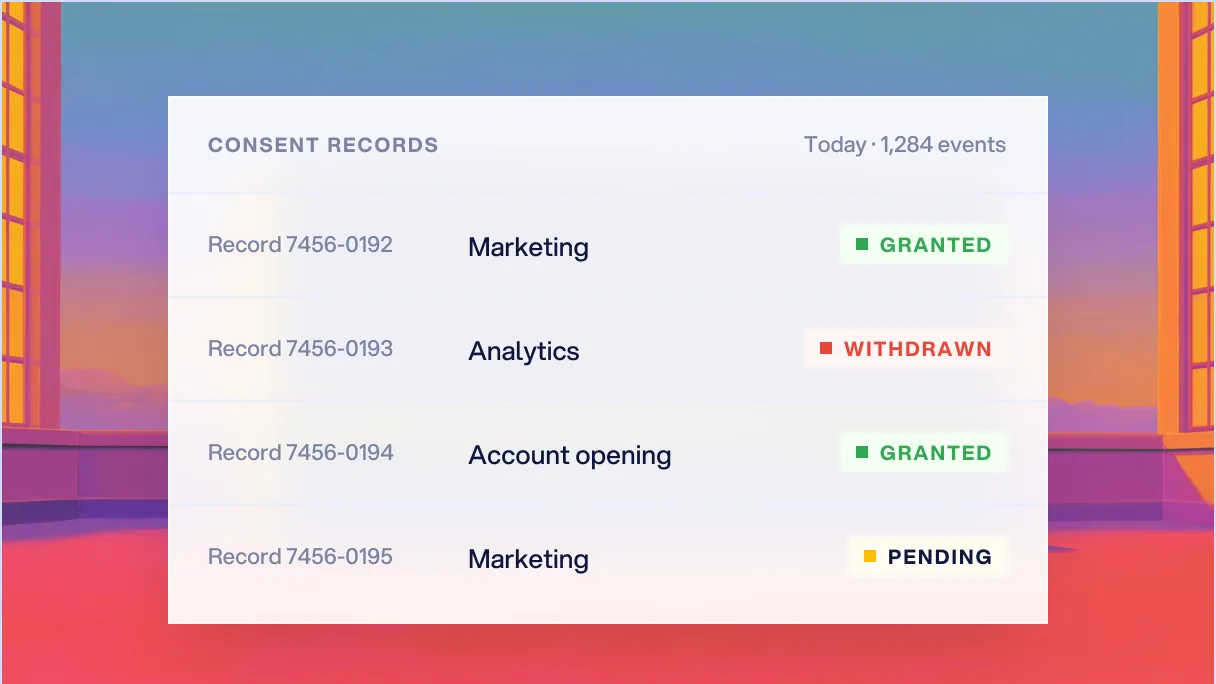
Every consent event, scan, assessment and answer is logged.
Version history
Each change kept, never overwritten.
Data stays in its source system
Discovery returns findings and metadata, never a copy of the record.
Data residency
Choose the region your data is hosted in.
Bring your own AI keys
Available when Redacto runs inside your own cloud account.
Human approval on risk
Anything that carries risk waits until a named reviewer signs off.
Trusted by the people who own data risk
“Our vendor security and privacy reviews used to live in spreadsheets and long email threads. With Redacto, every assessment, every piece of evidence and every follow-up sits in one place. When a customer sends us a security questionnaire, we answer it from that same record. We focus on the vendors that actually carry risk, and the paperwork no longer runs the week.”
“Privacy across a group of businesses is hard because every team has its own systems and its own idea of what personal data it holds. Redacto gave us one view of where personal data is collected, why we collect it and where it goes. When a customer request or an audit question comes in, I answer it with evidence, not a round of emails.”
“As a product team, we had one worry: would privacy compliance hurt the onboarding journey? It didn't. Redacto's consent flows fit into our app with very little engineering effort, and we change notices from the console instead of shipping a new build. Our users get a clear choice at every step, and we get a consent record we can stand behind.”
See it against your own data
Thirty minutes. We map one of your processing activities end to end.
Tell us where to send the invite. The message is optional.